Posts
Clickjacking太猥琐了
3389的SHIFT后门自动扫描[自动关闭错误连接]
鬼仔注:对 3389的SHIFT后门自动扫描 的补充
作者: cloie
#!/usr/bin/perl

use warnings;
use Win32::GUI;

use constant WM_CLOSE           => 16;

sub monitor {
my $handle = Win32::GUI::FindWindow('', '中断远程桌面连接');
Win32::GUI::SendMessage($handle, WM_CLOSE, 0, 0);
}
Scully: SQL DB interface and Brute Forcer
Scully is a brute forcer and a simple client interface to MSSQL and MYSQL Database servers. No more need to install database client libraries or setup ODBC connections in windows
What Does Scully do?
Scully is a client interface to MSSQL and MySQL database servers. No more need for
MSSQL/MySQL client libraries to be installed and no more need to setup an ODBC connection
either. Simply add IP/Hostname, username, password, port and database name and SQL away.
Google给我Blog生成附加链接了
Google对附加链接的说明:( 详细 )
Google 有时会根据网站内容生成附加链接以帮助用户浏览您的网站,这种链接称为网站链接。Google 会定期通过网站内容生成这些网站链接。
由于我们的网站链接是动态生成的,因此此列表会随时变化。
值得高兴的一件事。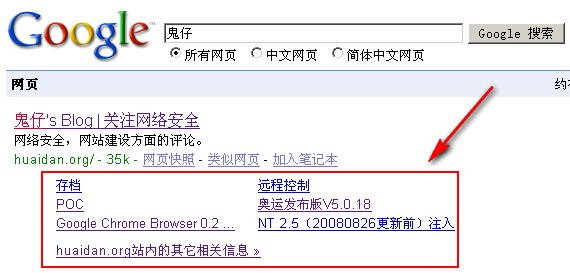
reDuh: Re-inventing TCP like its 1973!
reDuh was released as part of SensePost's BlackHat USA 2008 talk on tunnelling data in and out of networks. Most external firewalls block all incoming sockets except for port 80/443. reDuh allows an attacker to use the compromised web server as a tunneling proxy into the internal network enviroment. reDuh encodes data into valid HTTP requests, which is then delivered to the server agent, decoded, and redirects the data to the various configured tunnels. reDuh is available in JSP/PHP/ASP.
主页: reDuh home page
下载地址: reDuhClient (the local proxy)
| reDuhu Server Pages (JSP/PHP/ASP)
在 Way7T 那里看到的,原文题目为:超强的内网渗透跳板webshell。
入侵骗子站xuehk.com全过程
鬼仔注:本文的亮点在“仔细看过讨论后得知原来用nc反弹回来的shell权限是比webshell权限高的”这句,其实这个以前在 提权之道(关于WNDOWS 2003 目录权限的初探) 中就提到过---“反弹回来的SHELL的权限与网站的权限是不一样的”。
文章作者:落叶纷飞[J.L.S.T]
信息来源:安全叶子技术小组[J.Leaves Security Team] (http://00day.cn)
本文已发表于黑客手册0807期,转载请保留此信息.
这篇文章在两个多月前的时候我就完成了,但是只是做为我自己的入侵笔记来用,并没有想过要投稿。但现在因为比较急用银子,所以就发给N0h4ck献丑了。(为了有人对号入座,我把图片稍稍处理了一下,请读者们见谅)。
PHP二分法注射猜解
来源: wolvez
b.php
<?php
$conn = new com("ADODB.Connection");
$connstr = "DRIVER={Microsoft Access Driver (*.mdb)}; DBQ=". realpath("data.mdb");

$conn->Open($connstr);
$rs = new com("ADODB.RecordSet");
$sql="select * from news where id=".$_GET[id];
$rs->Open($sql,$conn,1,1);
if(! $rs->eof) {
echo "{ok}";
} else{
echo "{no}";
}
?>