ActiveX漏洞通用Exploit
作者:疯狗
终于在milw0rm找到了一个不错的shellcode,down&exec的,灰常好用!顺手写了一个C测试了下,结果是成功下载并执行了"木马",muma.exe是我用delphi写的一个简单的执行测试程序,无毒无害。
作者:疯狗
终于在milw0rm找到了一个不错的shellcode,down&exec的,灰常好用!顺手写了一个C测试了下,结果是成功下载并执行了"木马",muma.exe是我用delphi写的一个简单的执行测试程序,无毒无害。
By:疯狗【B.C.T】
忽然发现我仅仅是发掘ActiveX漏洞,但不去利用,利用远远要比发掘有趣:)
COMRaider自带了一个vuln.dll的漏洞链接库文件,我就拿这个下手吧(外面的AX漏洞要么已经被开发出exp,要么已经被找的差不多了...)
一共5个函数,我就用Method1参数进行攻击,字符型的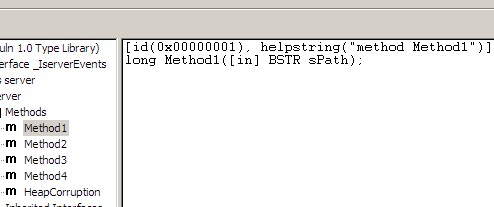
溢出点的定位我还是用CCProxy Telnet Proxy Ping远程栈溢出分析中的方法,首先生成1000个字符,然后提交到函数中,意料之中的崩溃,看看错误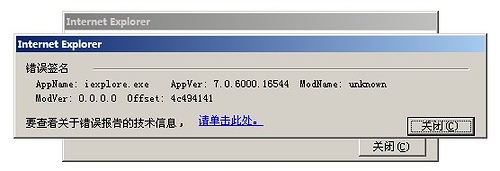
来源:酒水不犯茶水
好像10.5以下版本都中,这个似乎只能溢出一次,第一次溢出成功后,第二次开始会有realplay修复数据库的提示,点修复就中,取消不中
上次测试使用的"Windows 按钮突破专家" 4.5K 溢出没问题,但是"iecv.exe"那个87K
溢出的时候老是看不到界面,其实已经执行(进程中可以看到),不知道为什么(不知道是否大小问题)
另:IE5不中,代码中直接跳过了
http://www.blogjava.net/Files/baicker/realplay_071122_exp.rar
来源:Bug Center Team
作者:Maple-x
影响版本:
pplive 1.8beat2
有问题的dll:
MngModule.dll 1.7.0.2
未影响版本:
还没吧。:-)
分析:
以下是在luoluo的协助下分析的,基本属于luoluo语录。:)
给出分析过程,给和我一样刚接触溢出一点漏洞分析的思路。
来源:milw0rm
<!--
01/06/2007 23.19.50
Microsoft Windows DirectSpeechSynthesis Module (XVoice.dll)
/ DirectSpeechRecognition Module (Xlisten.dll)
remote buffer overflow exploit / 2k sp4 seh version
both the dlls are located in %SystemRoot%\speech folder
and they are vulnerable to the same issue.
while on 2k it depends on activex settings, under xp they are both
来源:milw0rm
6.30 10/06/2007
Microsoft Windows DirectSpeechSynthesis Module (XVoice.dll 4.0.4.2512)
/ DirectSpeechRecognition Module (Xlisten.dll 4.0.4.2512)
remote buffer overflow exploit/ xp sp2 version
both dlls are vulnerable, this is the poc for the first one
worked regardless of boot.ini settings, remotely and
by dragging the html file in the browser window