以前拿到一个,跟这个不一样,这个是黑鹰发出来的一个版本。
来源:黑鹰
大家好.我是jackal
2007给大家带点礼物.关于dz5.0的0day.
网上很多人发现了.只是没公布.
我不是第一个发现的.
但是自己读了代码找到了利用的地方.
******************************************************************************
本动画的MD5值为:
93b367244c68d61168a9cd6450b6362e DZ0day.exe
******************************************************************************
阅读全文 »
信息来源:邪恶八进制
##
# This file is part of the Metasploit Framework and may be redistributed
# according to the licenses defined in the Authors field below. In the
# case of an unknown or missing license, this file defaults to the same
# license as the core Framework (dual GPLv2 and Artistic). The latest
# version of the Framework can always
阅读全文 »
鬼仔:针对 Windows 2000 SP4 English 和 Windows 2000 SP4 English all updates on day 11.01.2007 下的 Microsoft Visual C++ 6.0 SP6 ,我这里是中文版的xp sp2。没办法测试,谁有合适的环境?测试下~
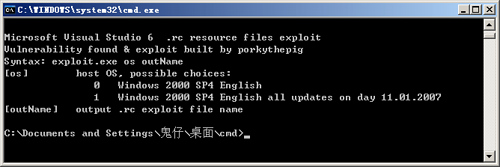
来源:milw0rm.com
阅读全文 »
鬼仔:我还没有测试,没有环境。。
来源:心路
这是LuoLuo写的EXP,他允许公布,所以我发一份到我的blog上面,他的blog地址为:http://luoluo.cnblogs.com/,这个EXP是用java写的,编译后作为applet插入到IE即可,测试了IE和FF均可成功。本EXP没有攻击性,成功之后运行计算器。如果有人修改之后用于攻击,后果自负。
阅读全文 »
来源:milw0rm.com
相关图片到 这里
去看。
另外还有注意说明:
tested on WinXP SP2 Korean version( fully patched except kb929969) & IE 6.0
sorry about that exploit hit ratio is only about 1/5
测试环境 WinXP SP2 韩文版,除了 kb929969 外,其他补丁齐全,IE 6.0
成功率只有1/5
阅读全文 »